BoG moves to regulate AI use in Ghana’s financial sector
By DL News
Published
2 min read
Speaking at the 43rd Annual General Meeting of the Ghana Association of Banks in Accra, Dr Asiama said artificial intelligence could significantly improve areas such as credit assessment, fraud detection, customer service, risk management a...
The Bank of Ghana is preparing a new regulatory directive to guide the use of artificial intelligence across the financial sector, as banks and other institutions increasingly adopt AI-driven technologies.
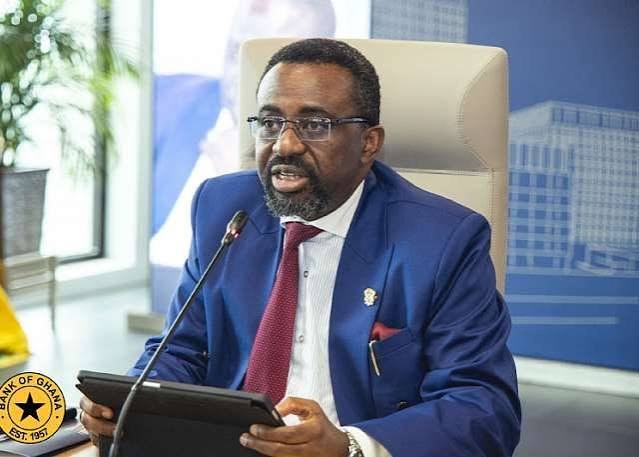
Governor of the Bank of Ghana, Dr Johnson Pandit Asiama, said the framework is intended to support innovation while ensuring that financial institutions manage the risks associated with the use of AI.
Speaking at the 43rd Annual General Meeting of the Ghana Association of Banks in Accra, Dr Asiama said artificial intelligence could significantly improve areas such as credit assessment, fraud detection, customer service, risk management and operational efficiency.
He, however, noted that the technology also presents challenges relating to cybersecurity, data quality, consumer protection and the reliability of automated models.
According to the Governor, the Bank’s regulatory approach will encourage responsible innovation while requiring appropriate controls and governance throughout the lifecycle of AI systems.
The planned directive forms part of a broader effort by the central bank to strengthen supervision as digital technologies continue to reshape the financial services industry.
Dr Asiama said the growth of digital financial services has contributed to greater convenience, efficiency and financial inclusion, but has also introduced new forms of operational and systemic risk.
He identified digital fraud, cybersecurity threats, data protection, cloud computing and reliance on third-party technology providers as areas receiving increased regulatory attention.
The Bank of Ghana is also working with the Ghana Association of Banks and other industry stakeholders on the implementation of its revised Cyber and Information Security Directive.
The central bank is expected to conduct thematic reviews to assess how financial institutions are complying with the revised cybersecurity requirements.
Dr Asiama urged boards and senior management of banks to treat cybersecurity and operational resilience as fundamental business risks rather than matters reserved solely for information technology departments.
He said financial institutions must continue to strengthen their governance structures, risk-management systems and business models as technology becomes more deeply integrated into financial services.
The Governor maintained that effective regulation must evolve alongside technological change to ensure that innovation contributes to a secure, resilient and sustainable financial sector.
Add a stronger news leadClarify the directive’s current status